One scan, shown whole.
5,288 files of Apache Fineract, read in one pass on 2026-08-20. Every figure below is that scan’s own output, including what it could not resolve.
Java 5,270 files · SQL 14 · Kubernetes manifests 4. Run 2026-08-20, one pass, no configuration beyond the repository URL.
Seventy findings, and which twelve are proven.
A rule matching a line is a candidate. A value the engine followed from the place it entered to the place it landed is a finding you can act on today. Both are shown, and they are never presented as the same thing.
A rule matching a line is a candidate. A value the engine followed from where it entered to where it landed is something you can act on today. The page never presents the two as the same thing.
22 unique findings across 70 occurrences.
| Rule | Severity | File | Line | Evidence |
|---|---|---|---|---|
| INPUT-001 | CRITICAL | …ueries/service/GenericDataServiceImpl.java | 228 | pattern |
| INPUT-001 | CRITICAL | …sAccountTransactionsSearchServiceImpl.java | 269 | pattern |
| INPUT-001 | CRITICAL | …sAccountTransactionsSearchServiceImpl.java | 117 | pattern |
| INPUT-001 | CRITICAL | …ies/service/DatatableWriteServiceImpl.java | 536 | pattern |
| INPUT-001 | CRITICAL | …ries/service/DatatableReadServiceImpl.java | 202 | pattern |
| PCI-4.1.1 | CRITICAL | …lient/feign/FineractFeignClientConfig.java | 177 | pattern |
| PCI-4.1.1 | CRITICAL | …lient/feign/FineractFeignClientConfig.java | 193 | pattern |
| PCI-4.1.1 | CRITICAL | …e/fineract/client/util/FineractClient.java | 514 | pattern |
| AUTH-001 | HIGH | …ganisation/staff/api/StaffApiResource.java | 102 | pattern |
| DPDPA-SVC-001 | HIGH | …AcmeExternalEventSourceProviderConfig.java | 29 | pattern |
| IAC-K8S-NETPOL-001 | HIGH | …tes/fineract-mifoscommunity-deployment.yml | 1 | pattern |
| IAC-K8S-RUN-ROOT-001 | HIGH | kubernetes/fineractmysql-deployment.yml | 68 | pattern |
| IAC-K8S-RUN-ROOT-001 | HIGH | kubernetes/fineract-server-deployment.yml | 37 | pattern |
| IAC-K8S-RUN-ROOT-001 | HIGH | …tes/fineract-mifoscommunity-deployment.yml | 76 | pattern |
| NOTICE-001 | HIGH | …s/0002-mifosx-base-reference-data-utf8.sql | 291 | pattern |
| PII-001 | HIGH | …vice/OidcAppUserResolutionServiceImpl.java | 71 | traced |
Where the personal data in this repository ends up.
One graph over the whole codebase: 119 nodes, 39 edges, and 12 complete source-to-sink traces. 18 of the sinks carry no evidence of encryption.
18 of the 39 sinks carry no evidence of encryption. Every ribbon above is drawn in proportion to the node counts beside it.
What counts as personal data here, and under which law.
Discovered from the schema and the code, not from a questionnaire. Each carries its category, its sensitivity, and the regimes that reach it, which is what turns a field name into an obligation.
Four of ten advisories can touch regulated data.
Dependency advisories re-ranked by whether the vulnerable package is imported by a file that handles personal data. This is an import-level reachability proxy, not proof of exploitability, and it is labelled that way in the product too.
imported by a file that handles personal data no path to personal data
| Package | CVEs | Severity | Upgrade to |
|---|---|---|---|
commons-lang3 3.17.0 | 1 | MEDIUM | 3.18.0 |
jackson-databind 2.21.4 | 3 | MEDIUM | 2.21.5 |
activemq-client 6.1.8 | 2 | HIGH | no single version |
postgresql 42.7.11 | 1 | HIGH | 42.7.12 |
One row per package, not per CVE. jackson-databind carries three separate advisories against 2.21.4 and each publishes its own fix list; 2.21.5 is the lowest version that appears in all three. activemq-client has no version that clears both of its advisories, which is why it says so.
What you hand to whoever asked.
An SBOM, the egress inventory, and the erasure surfaces, each with its own gaps stated. A report that claims complete coverage of a codebase this size would be the least credible thing in the bundle.
27 could not be resolved against an advisory database. They are reported as not analysed, never as clean. Of the 7 findings, 7 have a published fix and 0 are known to be exploited.
Named recipients: Pinecone, Segment, Sentry, Weaviate. 13 destinations could not be named and are listed as unresolved rather than dropped.
24 surfaces in code, covering access and erasure. 2 elements have no erasure or access path at all, so the answer to “can you delete me” for those is no.
The same scan, on screen.
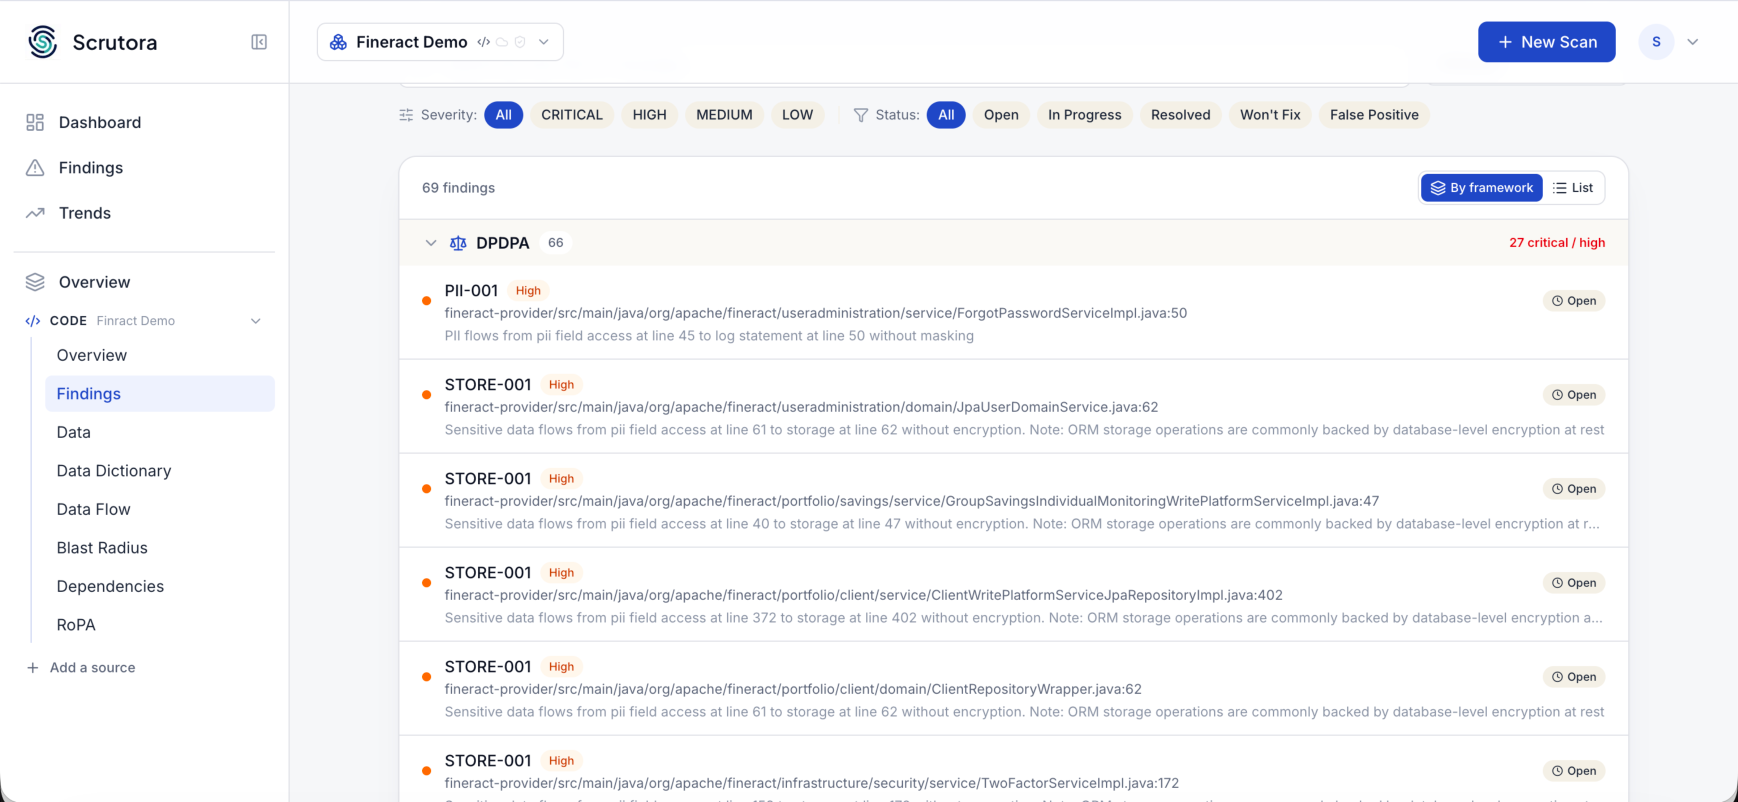
Findings group by the obligation they touch rather than by file, so the queue reads as a plan instead of a backlog. Every row opens into why it matters, the path the data took, and the line to change.
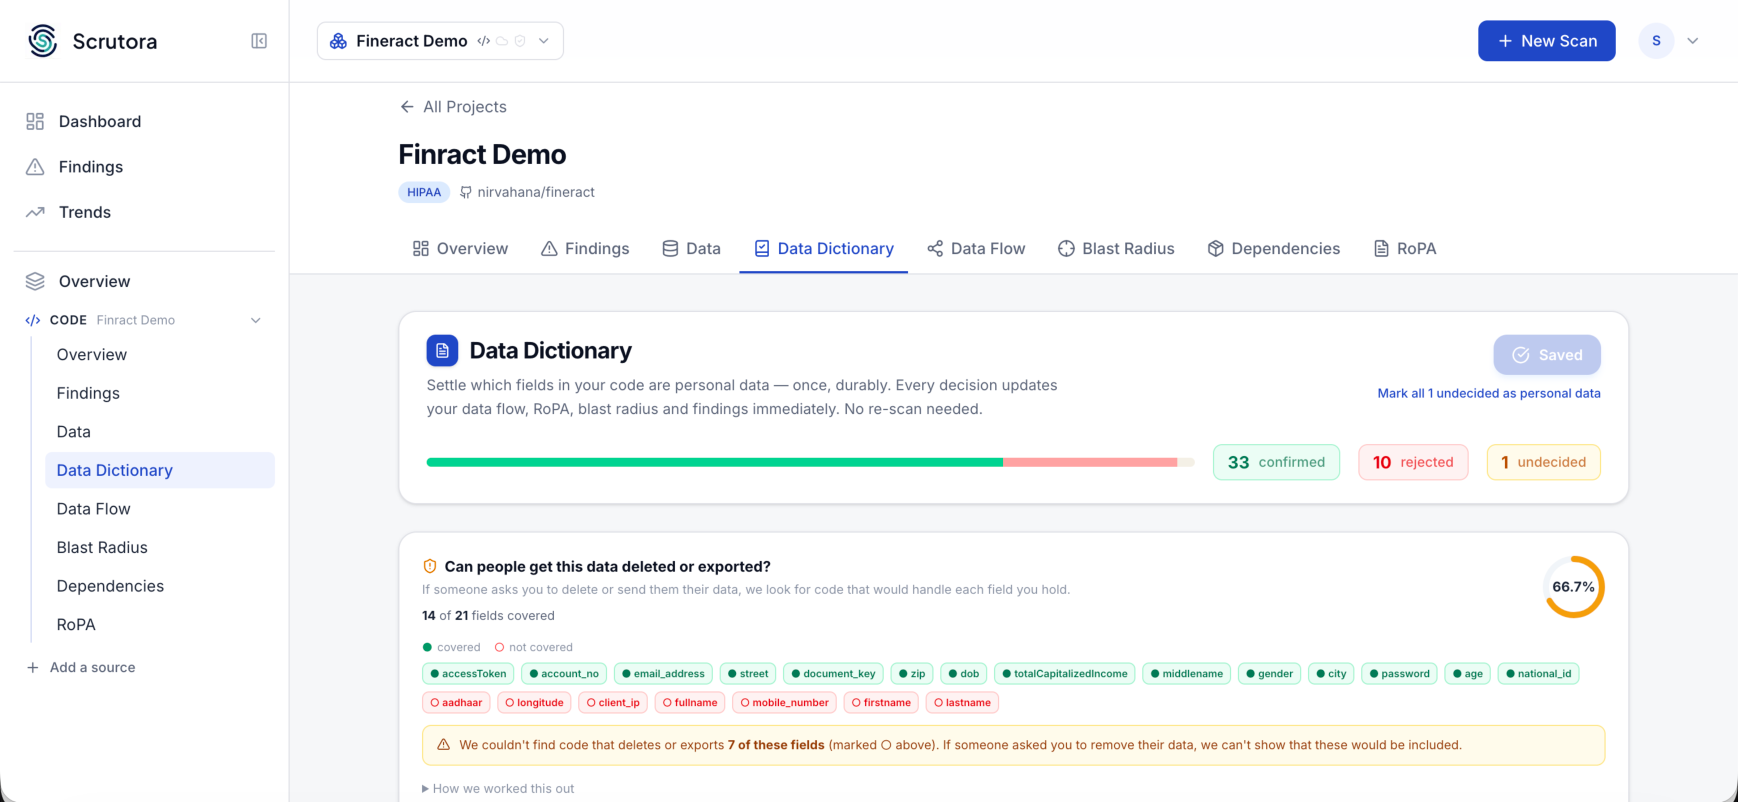
And the data dictionary, where a decision about what counts as personal data is made once and flows into the map, the RoPA, the blast radius and the findings together.