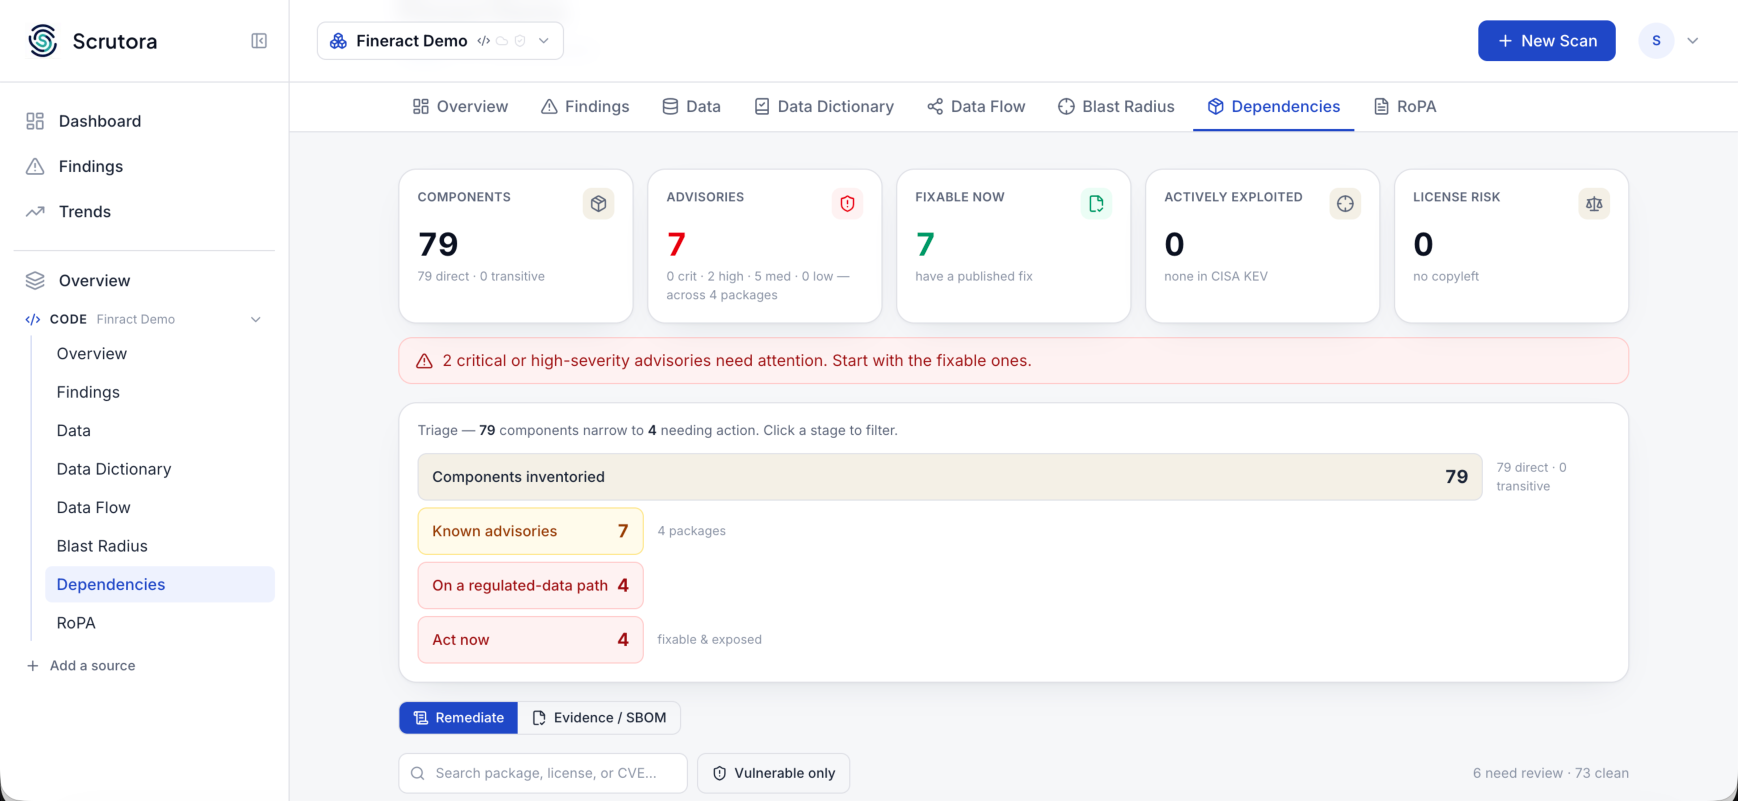
Seven advisories. Four that touch real data.
A CVE list ranks by severity, which is a property of the library. What you need is a property of your system: can this one reach personal data at all.
79
Components inventoried79 direct, 0 transitive
7
Known advisoriesacross 4 packages
4
On a regulated-data pathreachable from personal data
4
Act nowfixable and exposed
01 · The ranking
Sorted by what you can act on, not by score.
Actively exploited first, then reachable on a regulated-data path, then fixable, then severity. Severity alone puts an unreachable high above an exploited medium sitting on your customer table.
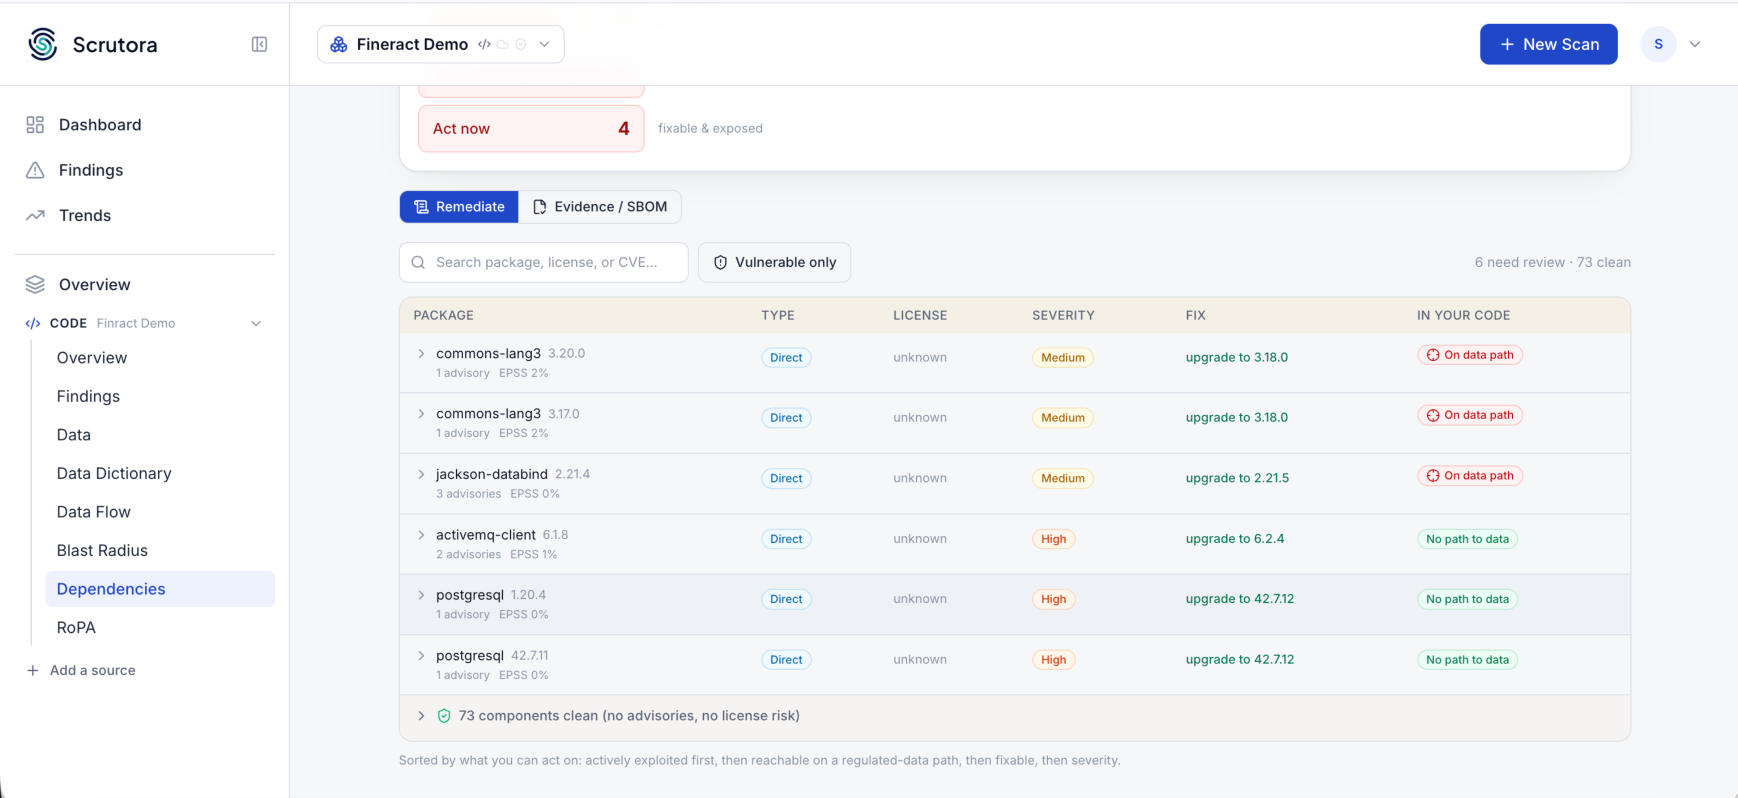
02 · The inventoryLICENCE RISK INCLUDED
An SBOM you did not have to assemble.